Friday, April 6, 2012
Russian Security Experts Analyze Backdoor.Flashback.39
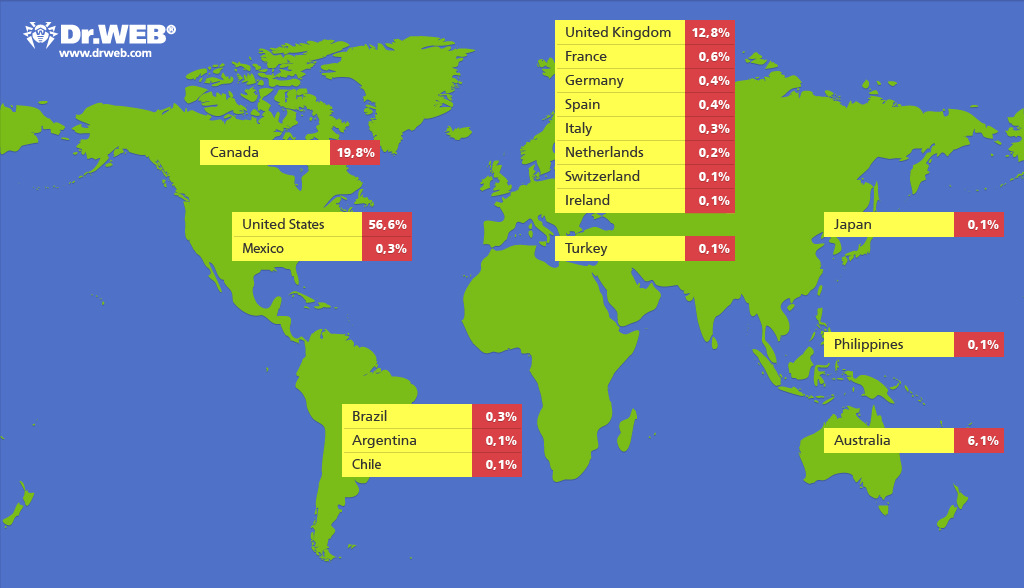
Security experts have found that even after Apple patched the flaw, the cybercriminals behind the operation didn't seem to be discouraged.
Researchers from Russian security firm Doctor Web analyzed the malicious element and determined that the infection begins when users are redirected to shady sites from compromised domains.
A piece of JavaScript code, placed on websites such as godofwar3.rr.nu, ironmanvideo.rr.nu, killaoftime.rr.nu, or gangstasparadise.rr.nu, loads the Java applet that contains the exploit.
The exploit then saves an executable onto the infected Mac machine. This executable file connects to a remote server from which it downloads and executes the final payload.
Continue Reading
Wednesday, March 23, 2011
Apple's software chief quits as iOS eats Lion
Thursday, November 4, 2010
Mac OS X Boonana Trojan Horse trojan.osx.boonana.a
Continue reading the SecureMac Security Bulletin
Tuesday, November 2, 2010
Yes, you need anti-virus on your Mac.. and now it’s free | Naked Security
Sophos has today announced the world's first free business-strength anti-virus program for home Macs. As Apple computers grow more popular than ever, they're an increasingly-enticing target for hackers (Windows users are still the number one target). And these hackers aren't just mischief-makers—by targeting your computer or applications you use, these criminals are out to steal and profit from your valuable personal information. Don't let them. Get Sophos Anti-Virus Home Edition for the Mac free today.
Friday, October 15, 2010
John Sculley On Steve Jobs, The Full Interview Transcript
Continue reading the full story at Cult of Mac by Leander Kahney
Thursday, October 14, 2010
Tuesday, June 1, 2010
OSX/OpinionSpy Spyware Installed by Freely Distributed Mac Applications
OSX/OpinionSpy is installed by a number of applications and screen savers that are distributed on sites such as MacUpdate, VersionTracker and Softpedia. The spyware itself is not contained in these applications, but is downloaded during the installation process. This shows the need for an up-to-date anti-malware program with a real-time scanner that can detect this malware when it is downloaded by the original application’s installer.
The information provided with some of these applications contains a misleading text that users must accept explaining that a “market research” program is installed with them, but not all of these specify this. Some of these programs are also distributed directly from developers’ web sites with no such warning.
The malware, a version of which has existed for Windows since 2008, claims to collect browsing and purchasing information that is used in market reports. However, this program goes much further, performing a number of insidious actions, which have led Intego to classify it as spyware.
For full technical details about OSX/OpinionSpy please visit the Intergo web site.
Saturday, April 17, 2010
The truth about Mac malware. It's a joke - War on Error - Blogs - Technology Blog and Community from IT Experts - Techworld.com
There are less then 200 Mac malware (that’s viruses, worms, Trojans, etc) programs. Having researched these a bit further as many were unfamiliar, I discovered that they are all years old, some going back as far as a decade or more. Study the list closely and you see that many of them are variants, that is slightly different versions of the same piece of code.
As impressively long as the list looks, this is in fact a fair chunk of ALL the malware that has afflicted the Mac in the last decade. Is this the best the Mac malware writers can do? One of the examples is a reheated virus from - no kidding - 1989."
"Apple antivirus company Intego has discovered a backdoor malware attack targeting Mac users OSX.HellRTS.D. As with so many of the small number of Mac-specific malware attacks that come up from time to time, this one is a variant of an attack from 2004, the company said, which will sound quaint to Windows users hit by thousands of variants on most days."
Posted using ShareThis
Thursday, April 8, 2010
Macintosh = Hacker-Proof?
Charlie A. Miller loves his Macbook Pro laptop. And his four other Apple ( AAPL - news - people ) PCs, the iPhone he uses daily and two older iPhones he keeps for tinkering. But his relationship with the company that created those gadgets is somewhat more complicated.
In March, for instance, the 36-year-old security researcher publicized his discovery of 20 security vulnerabilities in Apple's software. Each would allow a cybercriminal to take over the computer of a user who's tricked into opening a certain PDF attachment or who simply visits an infected Web page using Apple's Safari browser.
That haul of bugs is a record even for Miller, who over the last four years has become perhaps the world's most prominent Mac hacker. It may also be definitive proof that Apple devices aren't safe "right out of the box," as the company has claimed for years. "When I first began saying that Macs were less secure than Windows, everyone thought I was an idiot," says Miller. "So I had to prove it again and again and again."
In 2007 Miller became the first to hack the iPhone, using a flaw in its Safari browser to remotely gain control of the not-so-smart phone. Six months later he hacked a Macbook Air in two minutes at a competition in Vancouver. Last summer he revealed a method that allowed him to virally hijack the iPhone using text messages spread via a user's contact list.
Miller says his latest research doesn't aim to show off his elite hacking skills,most of which he learned over five years as a global network exploitation analyst for the National Security Agency. Instead, he wants to show just how easy it is to find chinks in the armor of commonly used software. Miller used a technique known as "dumb fuzzing" to find flaws. He ran the procedure more persistently than most hackers, leaving his fuzzing program to throw junk information at each target for three weeks before mining the data for exploitable flaws.
As for Apple, Miller says the company has learned to accept, if not appreciate, his work. He usually gives Apple weeks of notice before publicly describing its bugs. "They're always very polite," he says. "But I suspect they wish I didn't exist."
Read the full story at Forbes.com by Andy Greenberg
Updated:
Apple Patches Pwn2Own Bug
Friday, October 30, 2009
InfoWorld: Snow Leopard beats Windows 7
PC vs. Mac deathmatch: Snow Leopard beats Windows 7
"Windows 7 was built to fix the problems that plagued Vista, and it unquestionably succeeds in doing that. It's a bit less bloated, and it runs a bit faster. The annoying security alerts from User Account Control have been quieted. And the compatibility issues with third-party software and hardware device drivers have largely been ironed away; after all, it's been two and a half years since Vista debuted. Windows 7 even includes a virtual "XP mode" for running legacy programs.
[ Which is better? The Mac OS and Windows 7 UIs face off. | GetInfoWorld's 21-page hands-on look at the next version of Windows, from InfoWorld’s editors and contributors. | Find out what's new, what's wrong, and what's good about Windows 7 in InfoWorld's "Windows 7: The essential guide." ]
Windows 7 goes a few steps beyond merely repairing Vista. It borrows --and improves on -- tricks from the Mac's playbook to make it easier and faster to organize files and launch programs. Like Apple's operating system, Windows 7 not only looks good, but it has tools and shortcuts that help you work more efficiently. If there were ever a Windows that could challenge Mac OS X, Windows 7 is it.
Still, once you've had Mac, can you ever go back?"
Read the full story at InfoWorld